

Difference Between Ethical Hacking and Cyber Security
 Sep 16, 2026
RWn. Piyush Nakrani
Subject Matter Expert
Though ethical hacking and cyber security are interrelated, they do not mean one and the same thing. Both of them deal with the protection of computers, networks, applications, and data from cyber attacks. Nevertheless, these two concepts differ in terms of the approaches used.
Ethical hacking is aimed at identifying security flaws in information systems, whereas cyber security involves all the processes of protection against attacks and securing information systems, networks, applications, devices, and data.
The clarification of the difference between these two concepts may prove to be helpful for beginners and students.
What Is Cyber Security?
Cyber security refers to the techniques used to protect computer systems and information against any threat of security nature.
Beginners who want to build their knowledge in this broader field can explore a structured cyber security course covering core security concepts and practices.
The following are some of the duties of a cyber security team:
- Network security
- Application security
- Cloud security
- Data protection
- Identity and access management
- Endpoint security
- Security monitoring
- Incident response
- Risk assessment
- Security policies and compliance
For instance, an organization might implement such techniques as firewalls, access controls, encryption, monitoring, and security policies to secure its system. In case of an attack, the security team may perform an investigation of what happened and help to contain and restore systems.
Hence, cyber security involves both preventive measures and responses.
What Is Ethical Hacking?
Ethical hacking involves carrying out authorized assessments of systems and networks to detect any vulnerabilities which can be exploited by potential hackers.
Ethical hacking involves working with the authorization of the company owning the system. The objective of ethical hacking includes detecting vulnerabilities in the system and informing the owner about them.
Ethical hacking can include assessment of:
- Websites and web applications
- Networks
- Servers
- APIs
- Wireless networks
- Mobile applications
- User authentication systems
- Cloud environments
For example, an ethical hacker can assess if a company's website has any vulnerabilities that may permit the hackers to access the website. The ethical hacker notes this vulnerability and also gives the company some information on how to fix it.
Ethical hacking involves penetration testing, vulnerability assessments, and security testing.
Understanding how web applications are built can also be useful for security testing, and learning full stack development course provides exposure to both front-end and back-end technologies.
Difference Between Ethical Hacking and Cyber Security
The easiest way to understand the difference is to look at their scope.
| Factor | Ethical Hacking | Cyber Security |
| Main focus | Finding and testing vulnerabilities | Protecting digital systems and information |
| Scope | More specialized | Much broader |
| Main approach | Simulates attacks | Prevents, detects, and responds to threats |
| Typical work | Security testing and penetration testing | Security management, monitoring, protection, and response |
| Goal | Identify weaknesses before attackers do | Reduce security risks and protect systems |
| Common skills | Penetration testing, vulnerability testing, security tools | Networking, security controls, monitoring, incident response, risk management |
| Legal requirement | Requires authorization | Requires authorized access to systems and data |
| Career examples | Ethical hacker, penetration tester, security tester | Cyber security analyst, security engineer, incident responder |
Ethical Hacking Is a Part of Cyber Security
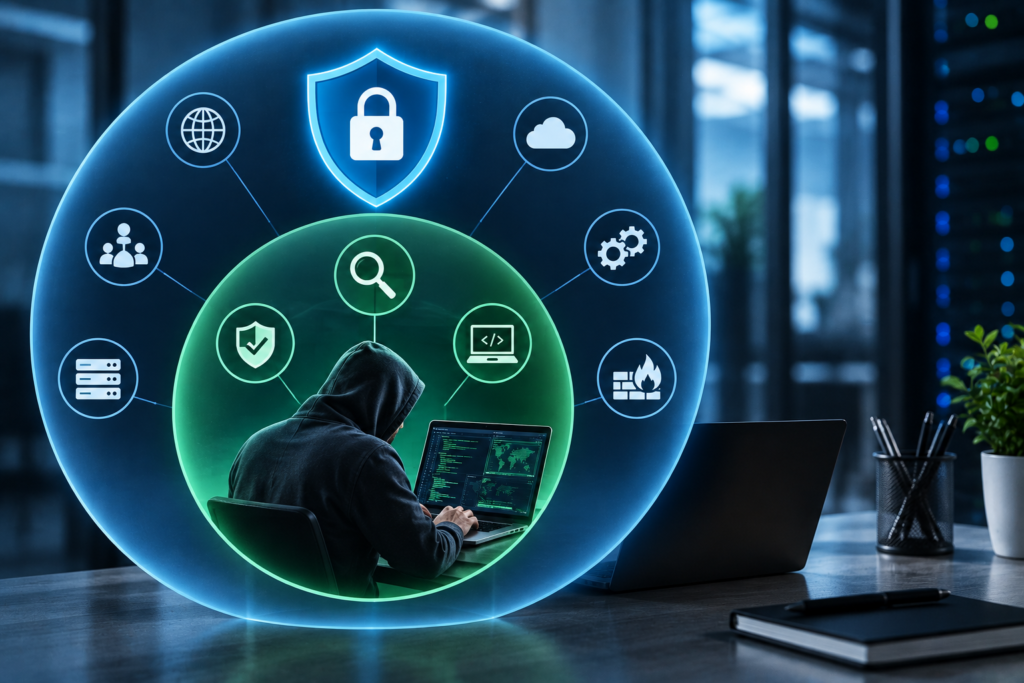
Another misconception about this is that ethical hacking and cyber security are different things. The reality is that ethical hacking is just a specific part of the broad subject of cyber security.
Consider the security of a business in terms of a building.
The job of cyber security is to secure everything in the whole building. This may encompass locks, cameras, entry regulations, alarms, surveillance, contingency plans, and other things.
Ethical hacking is more like engaging someone to test the security system in the building. They will search for weaknesses in the form of an unlocked door or some other flaw in the security.
The two subjects are often interconnected.
Key Responsibilities of an Ethical Hacker
The ethical hacker begins his hacking exercise by finding those systems that are acceptable for him to hack into. His testing procedure would include the following steps:
Once his hacking test is completed, he normally generates a report that details:
- The type of vulnerability that was identified
- Location of vulnerability
- Level of severity of the vulnerability
- Consequences of exploiting vulnerability
- How to fix the vulnerability
The exact activities depend on the scope and authorization given for the security test.
Working with large amounts of information also makes data analytics training useful for understanding patterns, identifying unusual activity, and supporting data-driven decisions.
Key Responsibilities in Cyber Security
Cyber security could be far more than just vulnerability assessment.
The cyber security professional might be involved in such activities as monitoring security alerts, configuring security controls, investigating any signs of malicious behavior, controlling access rights, endpoint protection, incident response, and helping organizations minimize security risks.
For instance, the security analyst monitors logs and alerts in order to detect any anomalies in the system’s behavior. In case of detection of some kind of attack, the analyst investigates the situation and helps to contain the threat.
However, planning and prevention are also crucial components of cyber security.
Skills Needed for Ethical Hacking
People interested in ethical hacking generally need a strong technical foundation.
Useful skills include:
- Computer Networking
- Basics of Linux & Windows
- Web Technologies
- Programming/ Scripting
- Access Controls & Authentication
- Vulnerability Assessment
- Penetration Testing
- Security Testing Tools
- Databases – Basics
- Documentation & Report Writing
Legal and ethical issues should also be taken into account by ethical hackers. Testing should only be done on those systems where appropriate permission is granted.
A strong understanding of software development fundamentals can also help learners understand how applications are built and where security weaknesses may occur.
Skills Needed for Cyber Security
Cyber security encompasses more career options, and hence the necessary skills vary depending on the job position.
Examples of these foundational skills include:
- Networking
- Operating systems
- Security principles
- Identity and access management
- Firewalls and other security controls
- Security monitoring
- Incident response
- Risk management
- Cloud security
- Data protection
Some roles are highly technical, while others focus more on security management, governance, risk, and compliance.
As security systems increasingly work with large datasets and automated detection methods, knowledge of data science and artificial intelligence course can also complement traditional cyber security skills.
Which Is Easier to Learn: Ethical Hacking or Cyber Security?
There cannot be a one-size-fits-all answer as both the domains span different areas.
Starting off as a beginner with some basics in cyber security would help lay a good foundation in the area.
Networking, operating systems, authentication, basic vulnerabilities, security concepts all make it easier to understand ethical hacking.
The technical aspect of ethical hacking becomes difficult due to the fact that penetration testing is done through knowledge of applications, networks, and operating systems.
However, cyber security being a large area means you may have to learn many other domains to become proficient at it.
Ethical Hacking vs Cyber Security: Which Career Is Better?
Neither is necessarily the best option; it really just comes down to your own preference.
Ethical hacking may suit you if you enjoy:
- Identifying Technical Flaws
- Testing Security
- Solving Problems
- Knowledge about How Attacks are Done
- Using Penetration Testing Tools
- Studying Methods for Exploiting Systems
Cyber security may suit you if you prefer:
- System and network protection
- Security event monitoring
- Incident investigation
- Control management
- Risk assessment
- Cloud security
- Infrastructure security
- More diverse security jobs
Neither does there exist any reason for separating the two as independent professions. A cyber security professional can learn how to become an ethical hacker, while an ethical hacker can diversify his area of expertise in cyber security.
Career Opportunities
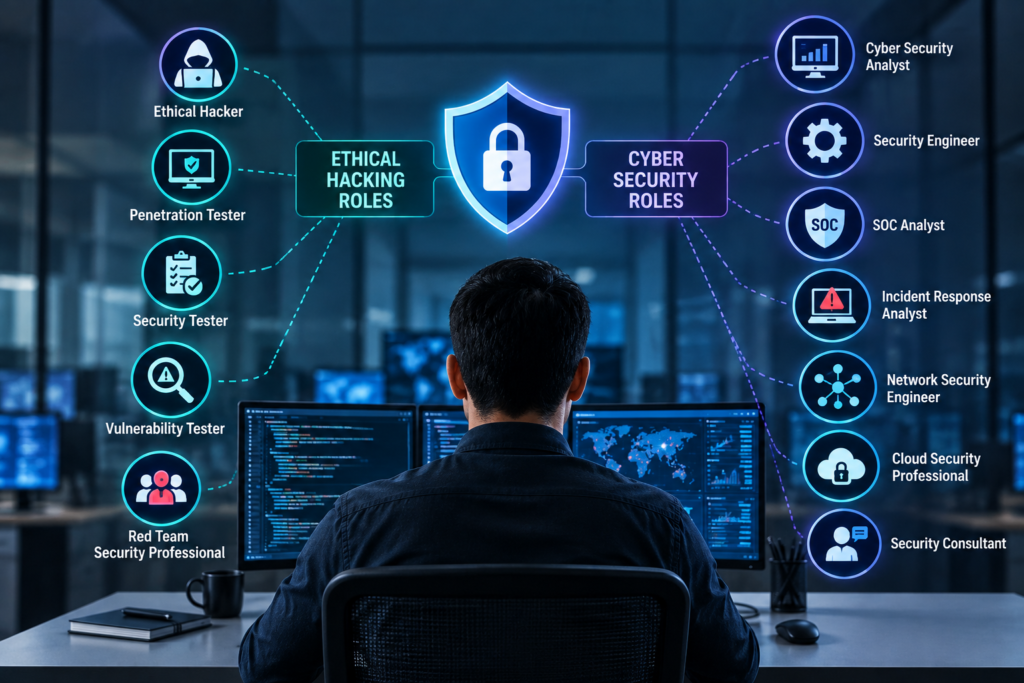
There could be various roles based on ethical hacking and cyber security.
Various roles related to ethical hacking include:
- Ethical Hacker
- Penetration Tester
- Security Tester
- Vulnerability Tester
- Red Team Security Professional
Broader cyber security roles include:
- Cyber Security Analyst
- Security Engineer
- SOC Analyst
- Incident Response Analyst
- Network Security Engineer
- Cloud Security Professional
- Security Consultant
The exact job title and responsibilities vary between organizations.
Summary
The main difference between ethical hacking and cyber security lies in their scope.
While ethical hacking revolves around security testing, cyber security encompasses the protection of systems, networks, applications, devices, and information from cyber attacks.
If one wants to test systems and learn about vulnerabilities exploitation, then ethical hacking could be a good specialization for that. If one desires to have a range of choices of security tasks, then cyber security is the way to go.
For starters, studying networking, operating systems, basics of security, and cyber threats would be useful before focusing on more advanced topics such as ethical hacking.